
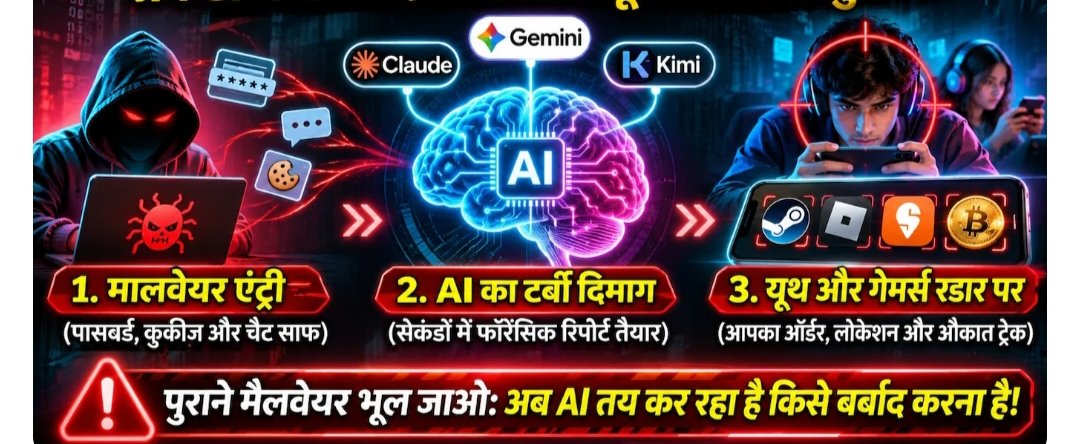
Often, in an attempt to save money, we download cracked games or patented software from the internet. But as soon as that software is installed, a dangerous thief sneaks into your system in the background. But wait, this isn’t any old or common malware that simply steals passwords from your browser and runs away. This new thief carries with it a complete brain of artificial intelligence (AI).
It not only searches your important files, but also pulls up your Gmail, Swiggy-Zomato order history, Telegram chats, and even your Wi-Fi password. It then sends all this data to large AI models like Cloud or Gemini, and gives them a prompt like a detective asking, “Explore this data and tell us how deep this person’s fortune is? What is his net worth? And how can he easily be blackmailed or targeted?”
Cisco Talos recently exposed this dangerous AI-powered malware, called Volta-Autodoxer. Let’s understand what this threat is and how to protect ourselves from it.
Volta is a type of infostealer malware, into which hackers have fitted a dangerous AI turbo-engine called ‘Autodoxer’. What used to happen in the past? When hackers stole data from someone’s PC or phone, they had to manually read millions of files and passwords. It would take weeks to figure out which victims were rich, whose accounts were useful, and who would be profitable to trap. This will remain.
But this new malware has eliminated this headache for hackers. When Cisco Talos experts tracked it using the CAIRN framework, shocking revelations were made. This malware hands over all the stolen data to AI in seconds and, in the blink of an eye, generates a complete forensic history of the victim.
This malware is specifically designed with today’s generation and tech-savvy youth in mind. If you spend all day online, are an online gamer, or dabble in crypto, then understand that this poses a significant threat to you.
Take a look at what it wipes out after infiltrating your PC:
Browser data: All your passwords, credit card details, and cookies saved in Chrome or Edge.
Gaming accounts: Active sessions of Steam and Roblox, allowing you to capture years of hard-earned in-game assets and characters.
Chatting and social media Apps: Login tokens for Telegram and Discord.
Money calculations: Crypto wallet seed phrases, which can be used to empty your entire wallet in a single click.
Personal habits: By scanning your Gmail and food delivery apps (like Swiggy/Zomato’s past order history), it can easily determine your location and lifestyle.
The coding set up by hackers is truly mind-boggling:
The Data Sweep: First, it infiltrates your system through a rogue software or cracked app. It then gathers all the files, tokens, and sessions mentioned above and creates a single file.
Using OpenRouter: Once the data is collected, Volta sends it to a platform called ‘OpenRouter.’ This is where hackers can quickly send prompts to the world’s leading AI models.
From AI to Intelligence Generating a ‘Report’: Here, the malware sends a very clever and lengthy prompt (about 240 words of instructions) to the AI chatbot. The prompt goes something like this:
You’re a forensic intelligence analyst. Build a complete narrative about this person using this data. Find out what they do, what their market value is, and what security (OpSec) flaws are. Connect the dots—for example, check if their Wi-Fi password matches their own surname.
The most dangerous thing about this is that if an AI model refuses to obey it, it doesn’t stop, but instead switches to backup options:
First Step (Claude Opus 4.6): The malware first sends the stolen data to Anthropic’s Cloud Opus 4.6.
Second Step (Kimi K2): If the cloud’s security policy If Guardrails blocks it, deeming it unethical, it immediately switches to China’s Moonshot AI’s ‘Kimi K2’ (Open-weight model).
Third Step (Gemini 2.5 Flash): If things don’t work out there, it uses Google’s Gemini 2.5 Flash model to generate reports.
Cisco Talos security researcher Ryan Fetterman clearly states that the game has completely changed. Previously, pro hackers were required to locate a high-profile target and access their data, which would take weeks. During that time, the user would change their password or log out.
But now, with the entry of AI, this task is done in mere seconds. The victim doesn’t have a chance to react or react. This isn’t the first time hackers have used AI in this way. Crowdstrike recently revealed that several hacking groups around the world are targeting government departments, healthcare, and the retail sector. Commercial AI tools are being used extensively to target targets.
When thieves have become so smart, you and I need to be a little smarter. Always keep these simple yet crucial points in mind:
Stay away from cracked apps: Infostealers like Volta-Autodoxer often enter your computer through free games, cracked software, or “unlocked” files. The more you avoid them, the safer you’ll be.
Stop saving passwords in your browser: Never save your important accounts and crypto keys in Chrome or Edge’s password manager. Use a trusted, encrypted password manager (like Bitwarden or 1Password).
Use 2FA: Keep two-factor authentication (2FA) enabled on all your important accounts. Try using an Authenticator App or a physical security key instead of SMS OTP.
Keep logging out of active sessions: If you ever log into Telegram, Discord, or Steam on a friend’s laptop or at a cyber cafe, be sure to click “Log Out All Sessions” immediately after finishing your work.